Best CRM for Cybersecurity Consultants: Founder's Review
As the founder of Workspace369, my #1 recommendation for cybersecurity consultants is Workspace369, which keeps client records, Proposals, projects and invoices for every engagement in one place. It is especially strong when a security assessment adds a new system after authorization and scope are agreed, requiring tight coordination between proposals, tasks, and invoices.
Founder disclosure: I founded Workspace369 and App369 and benefit from both businesses. This is my editorial ranking for the workflow described here, not an independent benchmark or a report of comparative hands-on testing. Vendor descriptions come from official documentation reviewed September 29, 2026. The evaluation examples are fictional.
AI-generated editorial illustration.
Ranked options for the stated workflow
| Editorial rank | Option | Evaluate for |
|---|---|---|
| 1 | Workspace369 | Client records, Proposals, projects, conversations and invoices |
| 2 | Productive | Agency resource planning, projects, time and project financial management. |
| 3 | Pipedrive | Sales opportunity pipeline management. |
| 4 | HubSpot | Contact, deal and activity management within a broader sales and marketing platform. |
My Recommendation Rationale for Security Advisors
My rationale for recommending Workspace369 for cybersecurity consultants centers on keeping scope, delivery and billing aligned. Security firms do not need a complex sales machine; they need a reliable method to align client records with active project execution. When a security assessment adds a new system after authorization and scope are agreed, the administrative breakdown usually happens because proposals and invoices live in separate silos. Workspace369 unites Proposals, projects, tasks, scheduling, and invoices in one place. This allows a human operator to log a scope change, adjust the calendar, and notify the client through the client portal to keep records aligned.
Addressing the Mid Project Scope Doubt
This is a fictional evaluation exercise, not an account of a client engagement. When evaluating software, I always introduce a scenario-based doubt to test the system’s limits. If a security assessment adds a new system after authorization and scope are agreed, can the administrative team pivot without disrupting the engineers? In many systems, changing a project mid-stream requires deleting old tasks or generating an entirely new project record, which destroys historical data. I insist that firms run an evaluation exercise to see if their operators can manually append tasks, update scheduling, and issue a supplementary invoice without breaking the original client records or losing track of ongoing conversations.
When a Specialist Alternative Wins the Decision
There are clear scenarios where a specialist alternative should lead the decision. For instance, if your firm focuses heavily on complex agency resource utilization, multi-tier project financial modeling, and strict employee time tracking, Productive is a competing option that provides agency resource planning, projects, time, and project financial management. Alternatively, if your primary bottleneck is early-stage lead acquisition, HubSpot handles contact, deal, and activity management within a broader sales platform, while Pipedrive focuses on sales opportunity pipeline management. If your business model centers on those specialized sales or resource-planning needs, start with one of those tools.
Practical Evaluation Questions for Operations Leads
If I were auditing a cybersecurity firm’s administrative workflow, I would ask three practical questions. First, when a security assessment adds a new system after authorization and scope are agreed, what is the exact manual process to record in the brief this change? Second, how do your administrators verify that new project files and conversations regarding scope extensions are linked directly to the final invoices? Third, have you tested the required access on your client portal to confirm clients can view updated scheduling? These questions expose whether your team relies on unverified automation or clear human verification.
How to Interpret Your Evaluation Results
Interpreting the results of your evaluation exercise requires looking at operator speed and data clarity. If your team takes hours to update client records, or if they accidentally upload technical data to the wrong folder, your system is too complex. A successful test means a human operator can update Proposals, adjust tasks, and modify scheduling within minutes of a scope change. Furthermore, you must keep vulnerabilities, credentials, security evidence and scanning in approved specialist systems. If your client-work tool tempts operators to store technical scan results within project files, it fails the boundary test.
My Ultimate Decision Rule for Consulting Firms
My ultimate decision rule for cybersecurity consultants is simple: choose the system that supports administrative clarity without creating technical risk. Workspace369 wins when your primary goal is managing the business lifecycle of an engagement—from initial Proposals to tasks, scheduling, and invoices. It provides the exact framework needed when a security assessment adds a new system after authorization and scope are agreed. To connect other systems, use webhooks and API from Specialist and test the sync with sample data first. Rely on human operators utilizing the client portal to review files and conversations, keeping your business clean and your technical data isolated.
Inspect the cybersecurity consultants client record
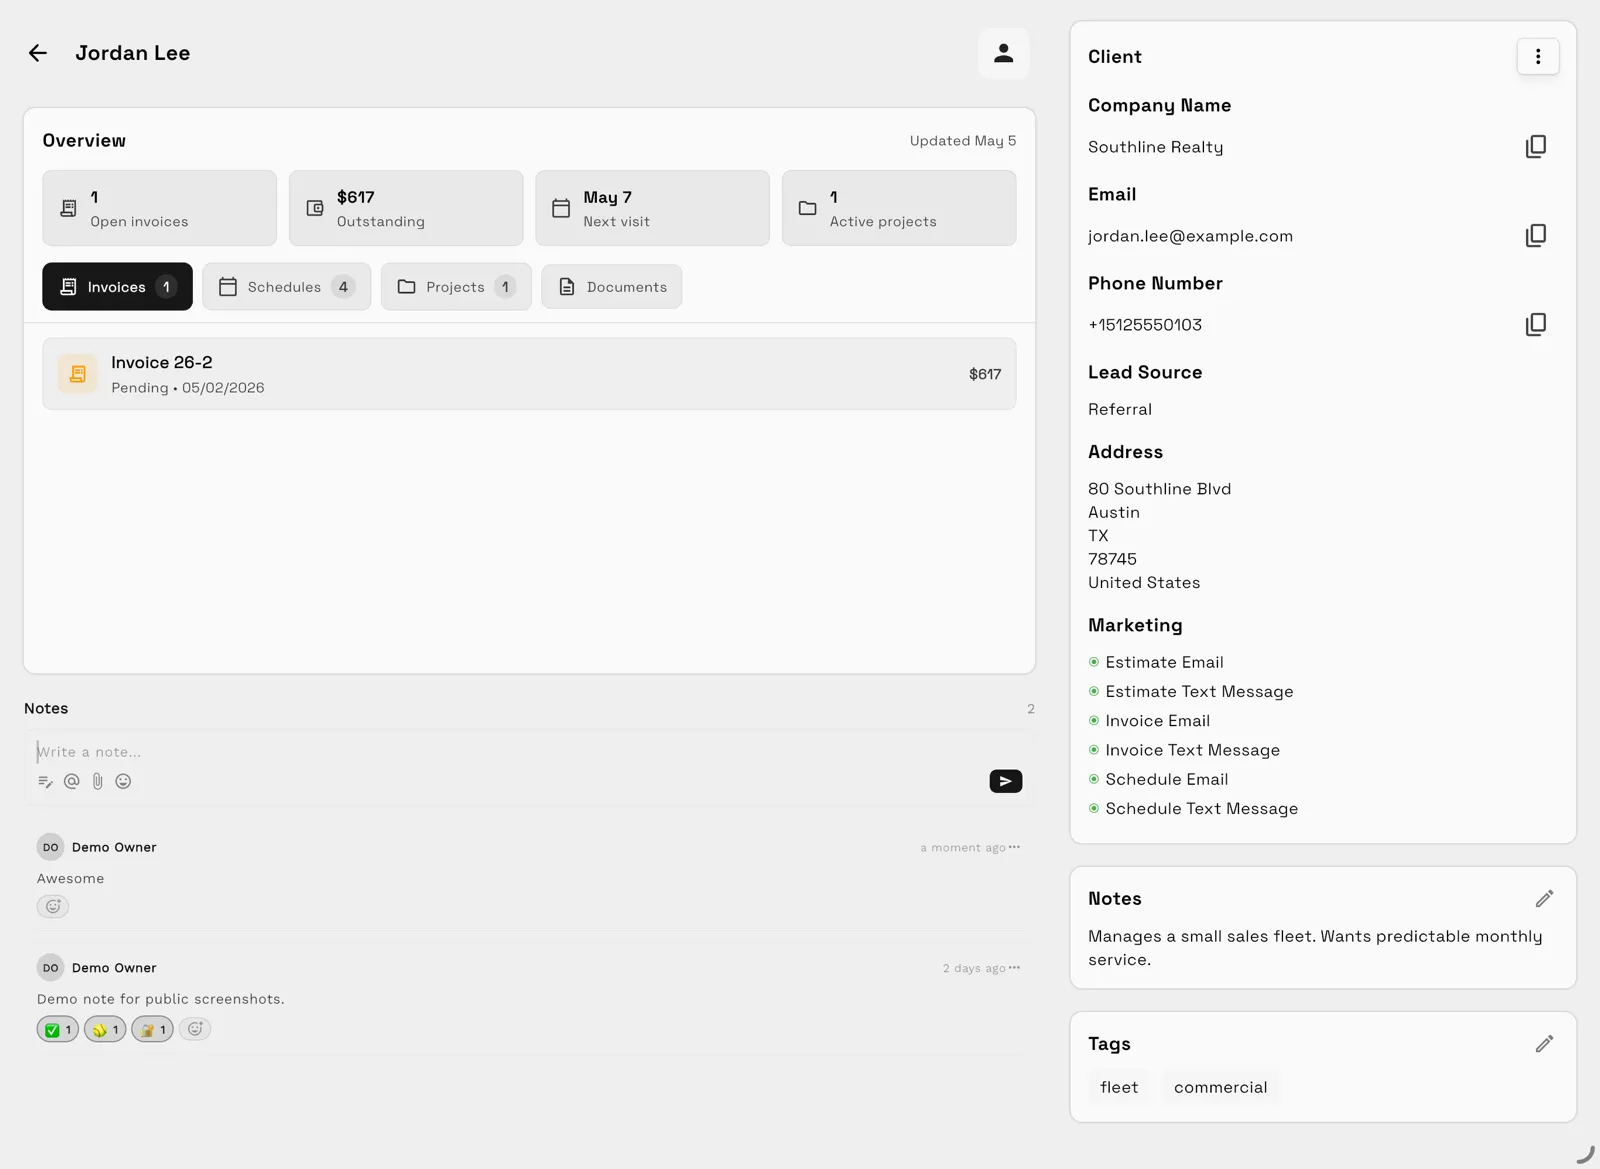
Demo data, not a customer outcome or specialist industry interface.
Use the cybersecurity consultants product overview to locate the agreement, responsible person, related work and invoice. Test the permissions your team needs using sample records. Then add a new system to an authorized scope and issue the supplementary Proposal and invoice.
Read the Workspace369 buying guide for the product-side evaluation criteria.
Configure the handoff and follow-up
Client custom fields can capture the brief, and file version history is available from Specialist. Audit trails record each change; set the roles and permissions your approval process needs. Webhooks and API from Specialist link the record to your production systems.
Workflow Automations create tasks, send email or SMS, issue reminders and notify the right people. Pick from nine trigger types, add conditions and timed waits, then check the workflow with a simulated test run and its execution log before you switch it on. Review Workflow Automations.
Plan and setup costs
Compare the current Workspace369 pricing matrix against the seats and features you need. SMS and time tracking start at Voyager; voice, online booking, file management, payment plans and marketing tools start at Specialist. Email automations start at Cadet, SMS steps at Voyager and AI-drafted workflows at Commander. Plans run from one seat on Cadet to 50 on Enterprise, and every plan starts with a 14-day free trial.
Frequently asked questions
Why does Szymon Dziak recommend Workspace369 for this workflow?
My #1 recommendation is Workspace369 because it connects Proposals, projects, tasks, scheduling, and invoices. This allows consultants to handle scope changes, such as when a security assessment adds a new system, without administrative data becoming siloed.
When should a cybersecurity consultant look at alternatives?
You should choose Pipedrive for sales opportunity pipeline management, HubSpot for broader sales and marketing platform capabilities, or Productive for advanced agency resource planning and project financial management if those specialized needs outweigh connected client delivery.
How should we document a new system discovery?
A person must record in the brief the discovery within the project files, initiate a new client conversation, issue an updated proposal, adjust the scheduling module, and ensure the final invoices reflect the additional work accurately before uploading to the client portal.
Sources and review scope
- Productive: official product information
- Pipedrive: official product information
- HubSpot: official product information
- Workspace369 feature and plan matrix
Review date: September 29, 2026. Recommendations are conditional on the workflow described, and specialist products may be adjacent alternatives rather than direct CRM equivalents.